
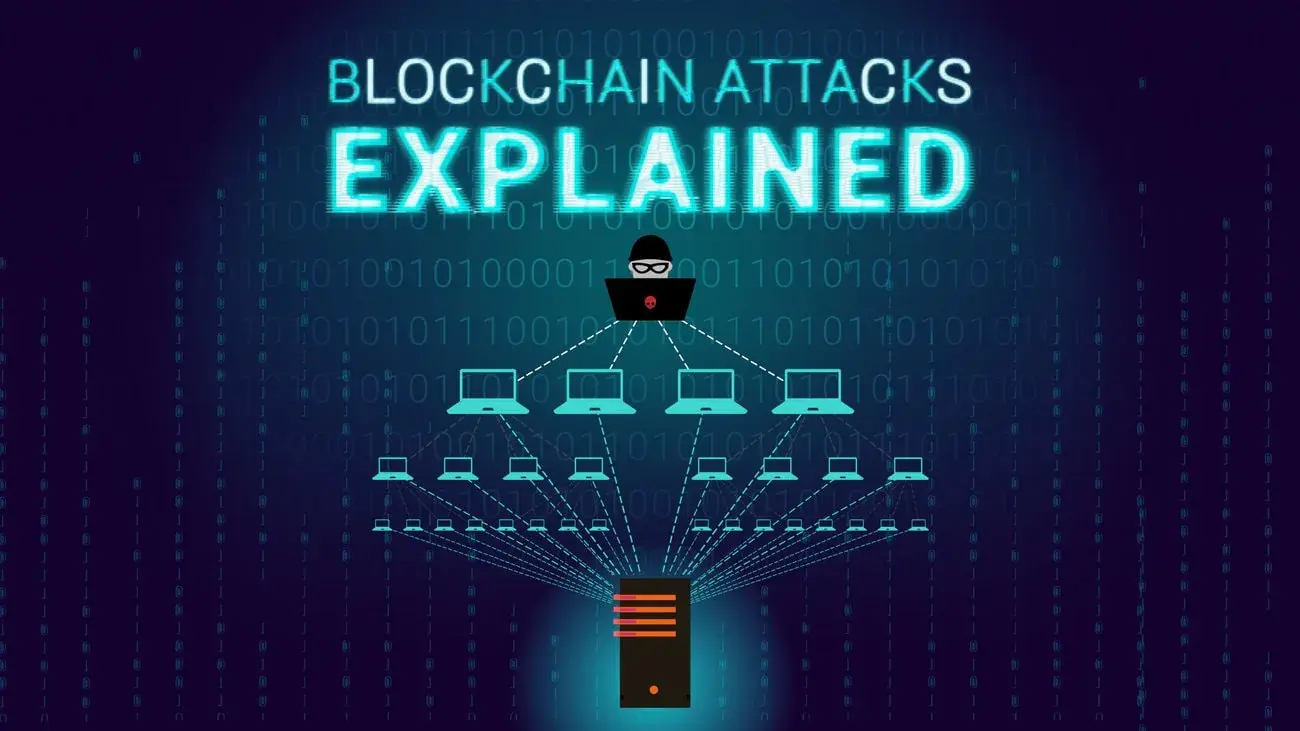
Blockchain security is layered. Consensus protects agreement on valid history, peer-to-peer networking propagates data, client software executes protocol rules, and applications add smart contracts, bridges, wallets and oracles. An incident at one layer should not automatically be described as the base blockchain being “hacked.”
The terms 51% attack, Sybil attack and denial-of-service attack describe different objectives. Their feasibility and impact depend on the exact consensus protocol and implementation; proof-of-stake is not simply proof-of-work with “staked coins” substituted for hash rate.
Blockchain attack terminology in 2026
| Attack | What the attacker seeks | What it does not automatically allow |
|---|---|---|
| Proof-of-work majority attack | Outpace honest hash power to reorganize recent blocks, double-spend the attacker’s coins or censor transactions | Forge signatures, spend arbitrary wallets or create invalid coins accepted by validating nodes |
| Proof-of-stake consensus attack | Use stake and message timing to delay finality, influence fork choice, censor or finalize conflicting history at protocol-specific thresholds | Ignore transaction signatures or application validity rules |
| Sybil attack | Create many identities to influence peer discovery, routing, voting or reputation systems | Gain consensus power where influence is weighted by scarce work or stake rather than identity count |
| Denial of service | Exhaust bandwidth, memory, CPU, storage, mempools or application resources | Rewrite ownership records merely by making a service unavailable |
Why “51%” is not a universal threshold
For a proof-of-work chain such as Bitcoin, majority hash power can make an attacker’s valid chain grow faster than the honest chain. Full nodes still enforce consensus rules, so miners cannot create an invalid transaction spending someone else’s coins without a signature.
Ethereum’s proof-of-stake documentation lists several thresholds: about 33% can prevent finality, 34% can under specific conditions cause double finality while risking severe penalties, more than 50% can dominate fork choice and censor or perform short reorganizations, and 66% can finalize the attacker’s preferred chain. Slashing, inactivity leaks and community coordination change both the cost and recovery path.
Sybil resistance and availability
Permissionless networks assume that one participant can create many identities. Proof of work and proof of stake are therefore Sybil-resistance mechanisms: influence is tied to a scarce resource rather than one vote per node. Other systems use identity checks, roles, fees, rate limits or reputation, each with different centralization and privacy tradeoffs.
Denial of service can target the peer-to-peer layer, transaction admission, a particular client bug, an RPC provider or one smart contract. Fees, per-peer limits, bounded resource use, multiple client implementations, redundant endpoints and incident-response procedures help, but decentralization does not make availability attacks impossible.
Original September 2022 blockchain-attacks guide (historical archive)
The original author-written sections below are preserved substantially intact. Its proof-of-stake “51%” analogy and claim that a January 2022 Solana outage was a four-hour BDoS incident are corrected above. The Solana example below now uses the Foundation’s official April 2022 account.
Based on principles of cryptography, decentralization and consensus, blockchain technology offers one of the strongest securities against traditional cyber attacks. However, it is not foolproof, even the strongest blockchains like Bitcoin and Ethereum have inherent vulnerabilities due to their infrastructure. In this article, we will look at the different types of attacks possible on a blockchain.
51% Attack
What is a 51% Attack?
A 51% attack, also known as a majority attack, is when a single person or a coordinated group controls over 50% of the hashing power on proof-of-work blockchains OR more than half of the validating power (staked cryptocurrencies) on proof-of-stake blockchains.
How does a 51% Attack work?
Since transactions on a blockchain are validated via consensus, owning 51% of the blockchain’s hashing power or staked crypto gives the attacker majority rule, effectively allowing them to take control of the network. In such a scenario, the attacker has the final say in the validation process, even if the other 49% are against it. This potentially causes network disruption in a number of ways:
- The attacker could reverse their own transactions, leading to a $1 problem.
- They could rewrite parts of the blockchain protocol, deliberately modifying the ordering of certain transactions.
- They can even prevent some or all transactions from being confirmed, denying other miners or validators from earning rewards, which results in a monopoly.
Limitations of a 51% Attack
On the other hand, a 51% attack does have its limits in the amount of disruption it can cause. While the attacker could reverse their own transaction, they cannot reverse other users’ transactions on the network. Moreover, given the immutable nature of the blockchain, the attacker cannot alter the functionality of block rewards nor create coins out of thin air (unless there is a bug in the smart-contract coding).
How likely will a 51% Attack happen?
While possible, a 51% attack is unlikely as it is extremely expensive to execute. Owning more than half of the network’s computing power or staked crypto could potentially cost millions or billions of dollars depending on the user population of the blockchain. This is why the bigger the network, the stronger the protection. A majority attack is virtually impossible to occur in leading blockchains such as Bitcoin, Ethereum and Binance Smart Chain.
But it is worth noting that the blockchain should be truly decentralized, on top of having a large userbase. This is because organizing a 51% attack would most likely be a coordinated effort. If several malicious actors collude and pool their resources together, then the network would be more centralized, which could potentially lead to a majority attack. This is more prevalent amongst smaller altcoin blockchains. Ethereum Classic (ETC), Bitcoin Gold (BTG), and Verge (XVG) were notable victims of the 51% attack.
Sybil Attack
What is a Sybil Attack?
A Sybil attack is when an attacker uses a single node to create and operate multiple fake accounts in order to gain disproportionate influence over decisions made in the network. It is a smaller variation of a 51% attack. The main difference is that a Sybil attack largely focuses on manipulating the number of accounts or nodes rather than already owning them. It also targets smaller areas in the blockchain, whereas a 51% attack is capable of taking over the entire network. However, in some cases, a successful large-scale Sybil attack can transition to a 51% attack.
The word “Sybil” derives from a case study about a woman named Sybil Dorsett, who was diagnosed with a Dissociative Identity Disorder, also known as Multiple Personality Disorder.
How does a Sybil Attack work?
A Sybil attack is quite difficult to detect and prevent, because most public blockchains do not have trusted nodes due to its decentralized nature. This means that the system perceives all nodes and accounts as real, even the fake ones. There are two scenarios of a Sybil attack:
- By creating numerous fake identities (or Sybil identities), the attacker will have enough capacity to out-vote the honest nodes on the network, allowing them to perform unauthorized actions in the system.
- The attacker can also control the flow of information in a network. If the attacker manages to obtain information about your IP address, they can create many fake nodes to surround you. They can then prevent you from receiving or transmitting blocks, effectively blocking you from using the network.
How to prevent Sybil Attacks?
Although a lot of time and research went into figuring out a way to detect and prevent Sybil attacks, there is still no guaranteed defense as of today. But there are some ways to help mitigate Sybil attacks:
- Identity validation techniques such as phone number, credit card or IP address verification can help reveal the true identity of hostile entities. This is a secure way to suss out fake accounts or bots for most types of peer-to-peer networks. However, this relies on a central authority to perform these identity validations which sacrifices anonymity for accountability. Moreover, this means that the validation authority could become a target for attack.
- Social trust graphs, on the other hand, can limit the extent of damage by a specific Sybil attacker, while maintaining anonymity. You can analyze connectivity data in social graphs like SybilGuard or SybilLimit to identify suspected Sybil clusters in distributed systems. But this technique is not perfect either, as small-scale Sybil attacks are more difficult to detect.
Blockchain Denial of Service Attack (BDoS)
Denial of Service Attack (DoS)
Before we go into Blockchain Denial of Service attacks (BDoS), let’s take a look at its predecessors.
Traditionally, a Denial of Service attack (DoS) or a Distributed Denial of Service attack (DDoS) when multiple computers are involved, is a malicious attempt to disrupt real users’ access to a website or network service by overloading its servers with a massive amount of traffic, causing the website or application to slow down its functionality or even crash entirely.
But for blockchains, a DoS or DDoS attack is difficult to execute, especially if the network’s userbase is large and decentralized. This is because a decentralized network distributes computing power worldwide, eliminating single points of failure such as servers or apps. Even if several nodes are down, the blockchain is able to continue operating and validating transactions, unless…
What is a Blockchain Denial of Service Attack (BDoS)?
With the rise of blockchain technology, a new type of DoS attack emerged — a Blockchain Denial of Service attack (BDoS). These attacks focus on the protocol layer of a blockchain, usually PoW blockchains, with the biggest threat being transaction flooding.
Since most blockchains have a fixed block size, there is a limit to how many transactions can fit into a block. Attackers can exploit this by spamming transactions to the blockchain, filling the blocks to prevent legitimate transactions from being added to the chain. The legitimate transactions remain in the public mempool waiting for the next block.
When this happens, the throughput capacity of the network is drastically slowed down, and in some cases shut down. Solana experienced a related resource-exhaustion incident in April 2022: its Foundation reported that NFT-mint bots flooded the network with roughly 6 million transactions per second and validators ran out of memory, but said there was no evidence of a denial-of-service attack.
How to prevent a Blockchain Denial of Service Attack (BDoS)?
Penetration testing is a core security auditing process that helps identify potential vulnerabilities before the mainnet is deployed. By simulating in-dept attacks, penetration testing offers traffic analytics tools that can help blockchain developers spot some of the telltale signs of a DoS attack such as unusual traffic patterns from a single IP address or IP range.
In our previous article, we have covered some of the top blockchain security auditing firms that offer the best penetration testing services.
Frequently asked questions
What is a 51% attack?
It commonly describes a proof-of-work attacker controlling most hash power so they can outpace the honest chain, reorganize recent blocks, double-spend their own coins or censor transactions.
Can a 51% attacker steal coins from any wallet?
No. Validating nodes still require valid signatures and enforce supply rules. Majority power can reorganize or censor valid transactions, not forge another user's private key.
Does every proof-of-stake attack require 51%?
No. Thresholds depend on the protocol. On Ethereum, one-third can delay finality, more than half can dominate fork choice, and two-thirds can finalize an attacker's preferred chain.
What is a Sybil attack?
A Sybil attack creates many identities to gain disproportionate influence over peer discovery, routing, voting, reputation or another identity-sensitive process.
How do blockchains resist Sybil attacks?
Permissionless networks commonly weight influence by scarce proof of work or stake instead of identity count. Other systems may use fees, roles or identity verification.
What is a blockchain denial-of-service attack?
It is an attempt to reduce availability by exhausting resources such as bandwidth, CPU, memory, storage, transaction queues or smart-contract execution.
Does decentralization prevent DDoS attacks?
No. Redundancy removes some single points of failure, but peer networks, clients, RPC providers and applications can still be congested or exploited.
Was Solana's April 2022 outage a DDoS attack?
The Solana Foundation reported extreme bot traffic and validator memory exhaustion but explicitly said there was no evidence of a denial-of-service attack.
Are smart-contract exploits consensus attacks?
Usually not. A contract exploit can execute valid transactions that abuse application logic while the underlying blockchain consensus continues operating correctly.
How can users reduce blockchain attack risk?
Wait for appropriate confirmation or finality, diversify critical infrastructure, verify contract and bridge risk, use secure wallets and monitor official incident channels.
Sources and further reading
- Ethereum.org: proof-of-stake attacks and defenses
- Ethereum.org: proof-of-stake consensus and finality
- Bitcoin whitepaper: chain selection and double-spend analysis
- NIST: blockchain and distributed-ledger technology concepts
- NIST: Web3 availability and denial-of-service risks
- Solana Foundation: April 2022 outage report and mitigation
Share
Found this useful?
Share it with someone who'd want to read it.
Related
Blockchain Security Guide: Wallets, Smart Contracts and Common Attacks
A practical blockchain security guide covering private keys, phishing, approvals, smart contracts, exchanges, consensus attacks and incident response.
Why Do Cross-Chain Bridges Keep Getting Hacked?
Out of all blockchain attacks , cross-chain bridges are one of the most targetted ones.
Top 10 Best Ways to Keep Your Cryptocurrencies Safe
In this article we give you the top 10 best ways to keep your cryptocurrencies safe.